Bloom Trading hit by $947K breach due to ‘third-party module,’ promises 100% reimbursement
ambcrypto.com
26 October 2026 19:19, UTC
Bloom Trading users suffered nearly $1 million in reported cryptocurrency losses after a suspected security breach drained dozens of Solana wallets on the 26th of October.
The incident affected 49 wallets, raising concerns about the security of Telegram-based cryptocurrency trading platforms.
Reportedly, an attacker drained 9,408 $SOL, valued at approximately $954,000.
Know when your coins move
Alerts, real-time prices, and market news — all in one app
Point your phone camera to install
4.8 based on 40K reviews in the App Store and Google Play
The incident involved the largest individual wallet loss of 1,636 $SOL (about $166,000), underscoring the gravity of the situation.
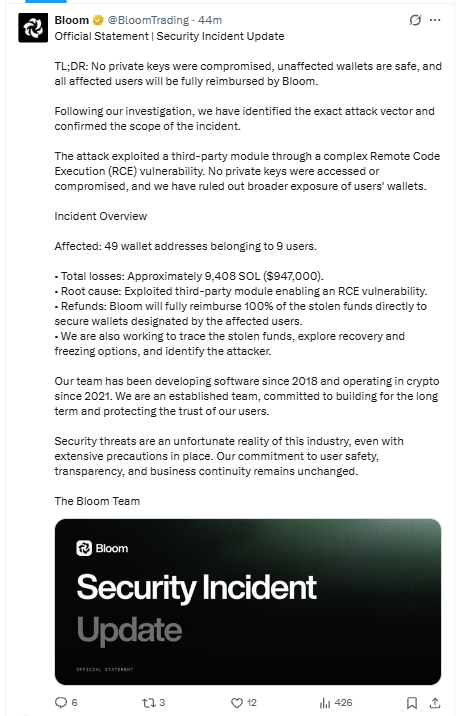
Bloom Trading later clarified that 49 addresses were affected, belonging to nine users.
After investigation, Bloom Trading found that the attack came from an exploited third-party module.
The vulnerability reportedly enabled remote code execution, which could allow for running commands in the software environment without authorization.
The company assured that wallets not affected were still safe, suggesting the breach was restricted to the identified addresses.
Source: Bloom on X
Bloom Trading promises 100% reimbursement
After confirming the cause of the attack, Bloom Trading reiterated its commitment to the compensation of all nine affected users.
The platform also stated that it would send the stolen money straight to newly created safe wallets, saying,
Bloom will fully reimburse 100% of the stolen funds directly to secure wallets designated by the affected users.
Beyond the reimbursement, the team had begun the process of tracing the stolen assets and considering recovery, which may involve fund freezes.
The company, however, was yet to specify when reimbursements would be completed.
Bloom rules out private-key exposure following investigation
The recent updates also answered questions regarding the wallet security practices of Bloom Trading.
Bloom is a trading automation service on the Telegram platform, which works with the Solana [$SOL] and Ethereum [ETH] Virtual Machine networks.
These types of platforms might be vulnerable to security threats because of software integrations, especially if third-party components have vulnerabilities that can be exploited.
Bloom’s investigation, however, attributed the incident to an RCE vulnerability, not to compromised private keys. .
The company stated,
No private keys were compromised, unaffected wallets are safe, and all affected users will be fully reimbursed by Bloom.
Bloom also emphasized its longstanding software development experience and commitment to maintaining business operations.
The incident came after several cryptocurrency security warnings were reported all over October.
Earlier, AMBCrypto reported a critical $XRP vulnerability that Ripple patched before attackers could exploit it.
The vulnerability might have allowed the theft of trillions of $XRP from just one transaction.
Separately, a suspected NBA Instagram compromise raised concerns after the account promoted a Solana-based memecoin.
While these incidents involved different security threats, they highlighted vulnerabilities across cryptocurrency infrastructure and digital platforms.
Final Summary
Bloom Trading traced the $947K theft to a third-party software vulnerability affecting nine users.
Full reimbursement is promised, but stolen fund recovery and compensation remain pending.

 ambcrypto.com