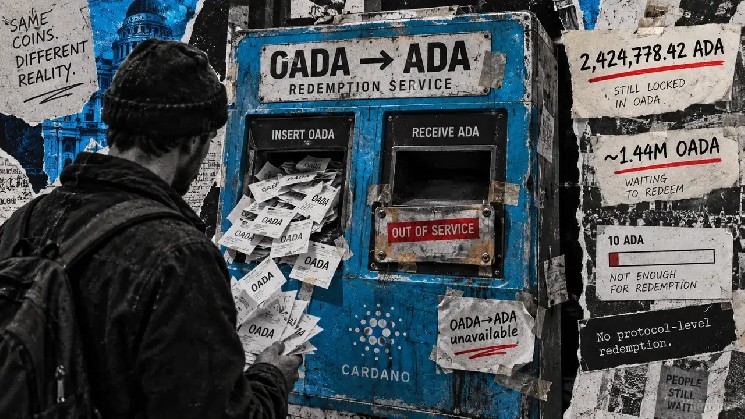
Those missing checks allowed the validator to accept a transaction after the tradable $ADA reserve had turned negative. Splash said a reserve-domain check or a two-sided fee bound would have stopped the reconstructed attack.
Either fix would close the documented exploit path. Neither would return the $ADA that had already left the pool. Immediately after the drain, the pool held 10 $ADA and about 1.44 million OADA, while its tradable $ADA reserve was negative and its LP token balance was unchanged.
The balance-sheet damage matters because Splash’s Sept. 13 snapshot said OADA had no protocol-level redemption. Other OADA venues in the report were close to empty at that time, with the listed pools holding only single- or double-digit $ADA balances.
The attacker’s OADA sale created another constraint. At 14:53 UTC on Sept. 13, a Minswap V2 OADA/FLDT pool held 1,763,923 OADA against 45,751 FLDT. Splash said new $ADA/OADA liquidity could be arbitraged against that inventory, allowing discounted OADA to compete for any fresh $ADA placed in a reopened pool.
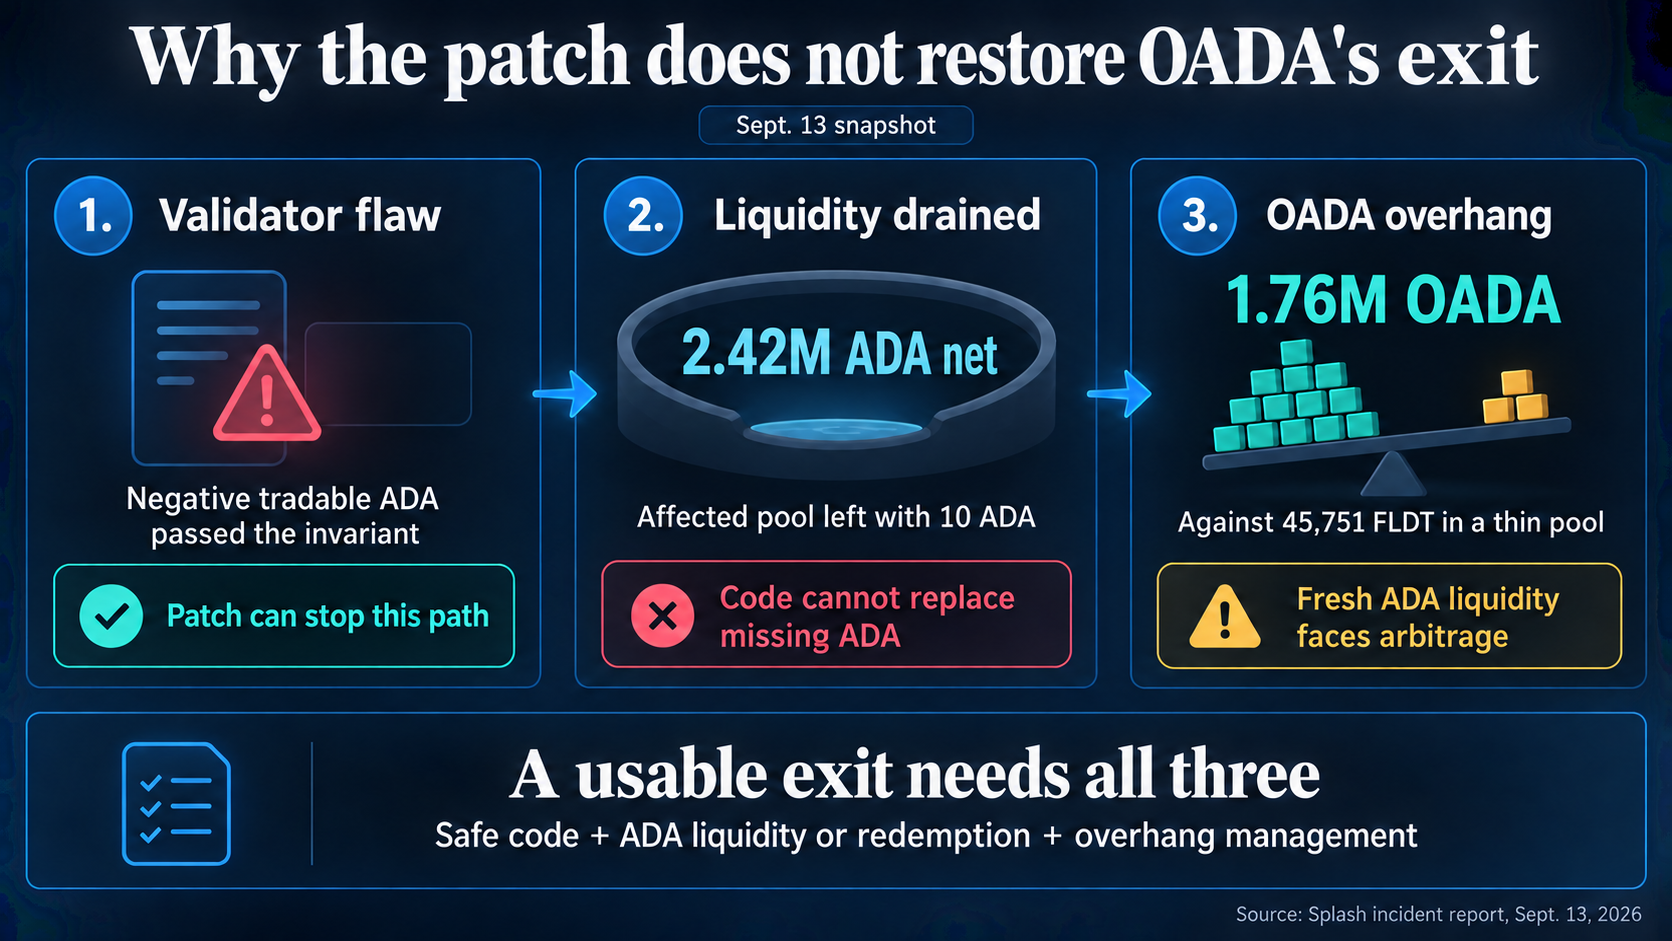
A code patch can stop the documented exploit path, but restoring an OADA exit also requires $ADA liquidity or redemption and management of the thin-pool OADA inventory.
A usable relaunch would therefore require more than corrected validator logic. It would need replenished $ADA liquidity or a protocol redemption mechanism, along with a way to address the OADA inventory in the thin secondary market.
Optim Finance said on Sept. 13 that its protocol was paused, remaining liquidity had been removed and OADA-to-$ADA swaps were unavailable. In a Sept. 15 update, it said it was indexing the chain and compiling a full accounting of impacted addresses and assets while working toward a resolution. That update did not announce restored liquidity, redemption or operations.

 cryptoslate.com