DOJ Disrupts North Korean Fake-Call Crypto Theft Scheme
thedefiant.io
17 h
The U.S. Justice Department said Thursday it seized cloud infrastructure used in a North Korean video-call impersonation campaign that stole more than $400 million in cryptocurrency over the past 18 months.
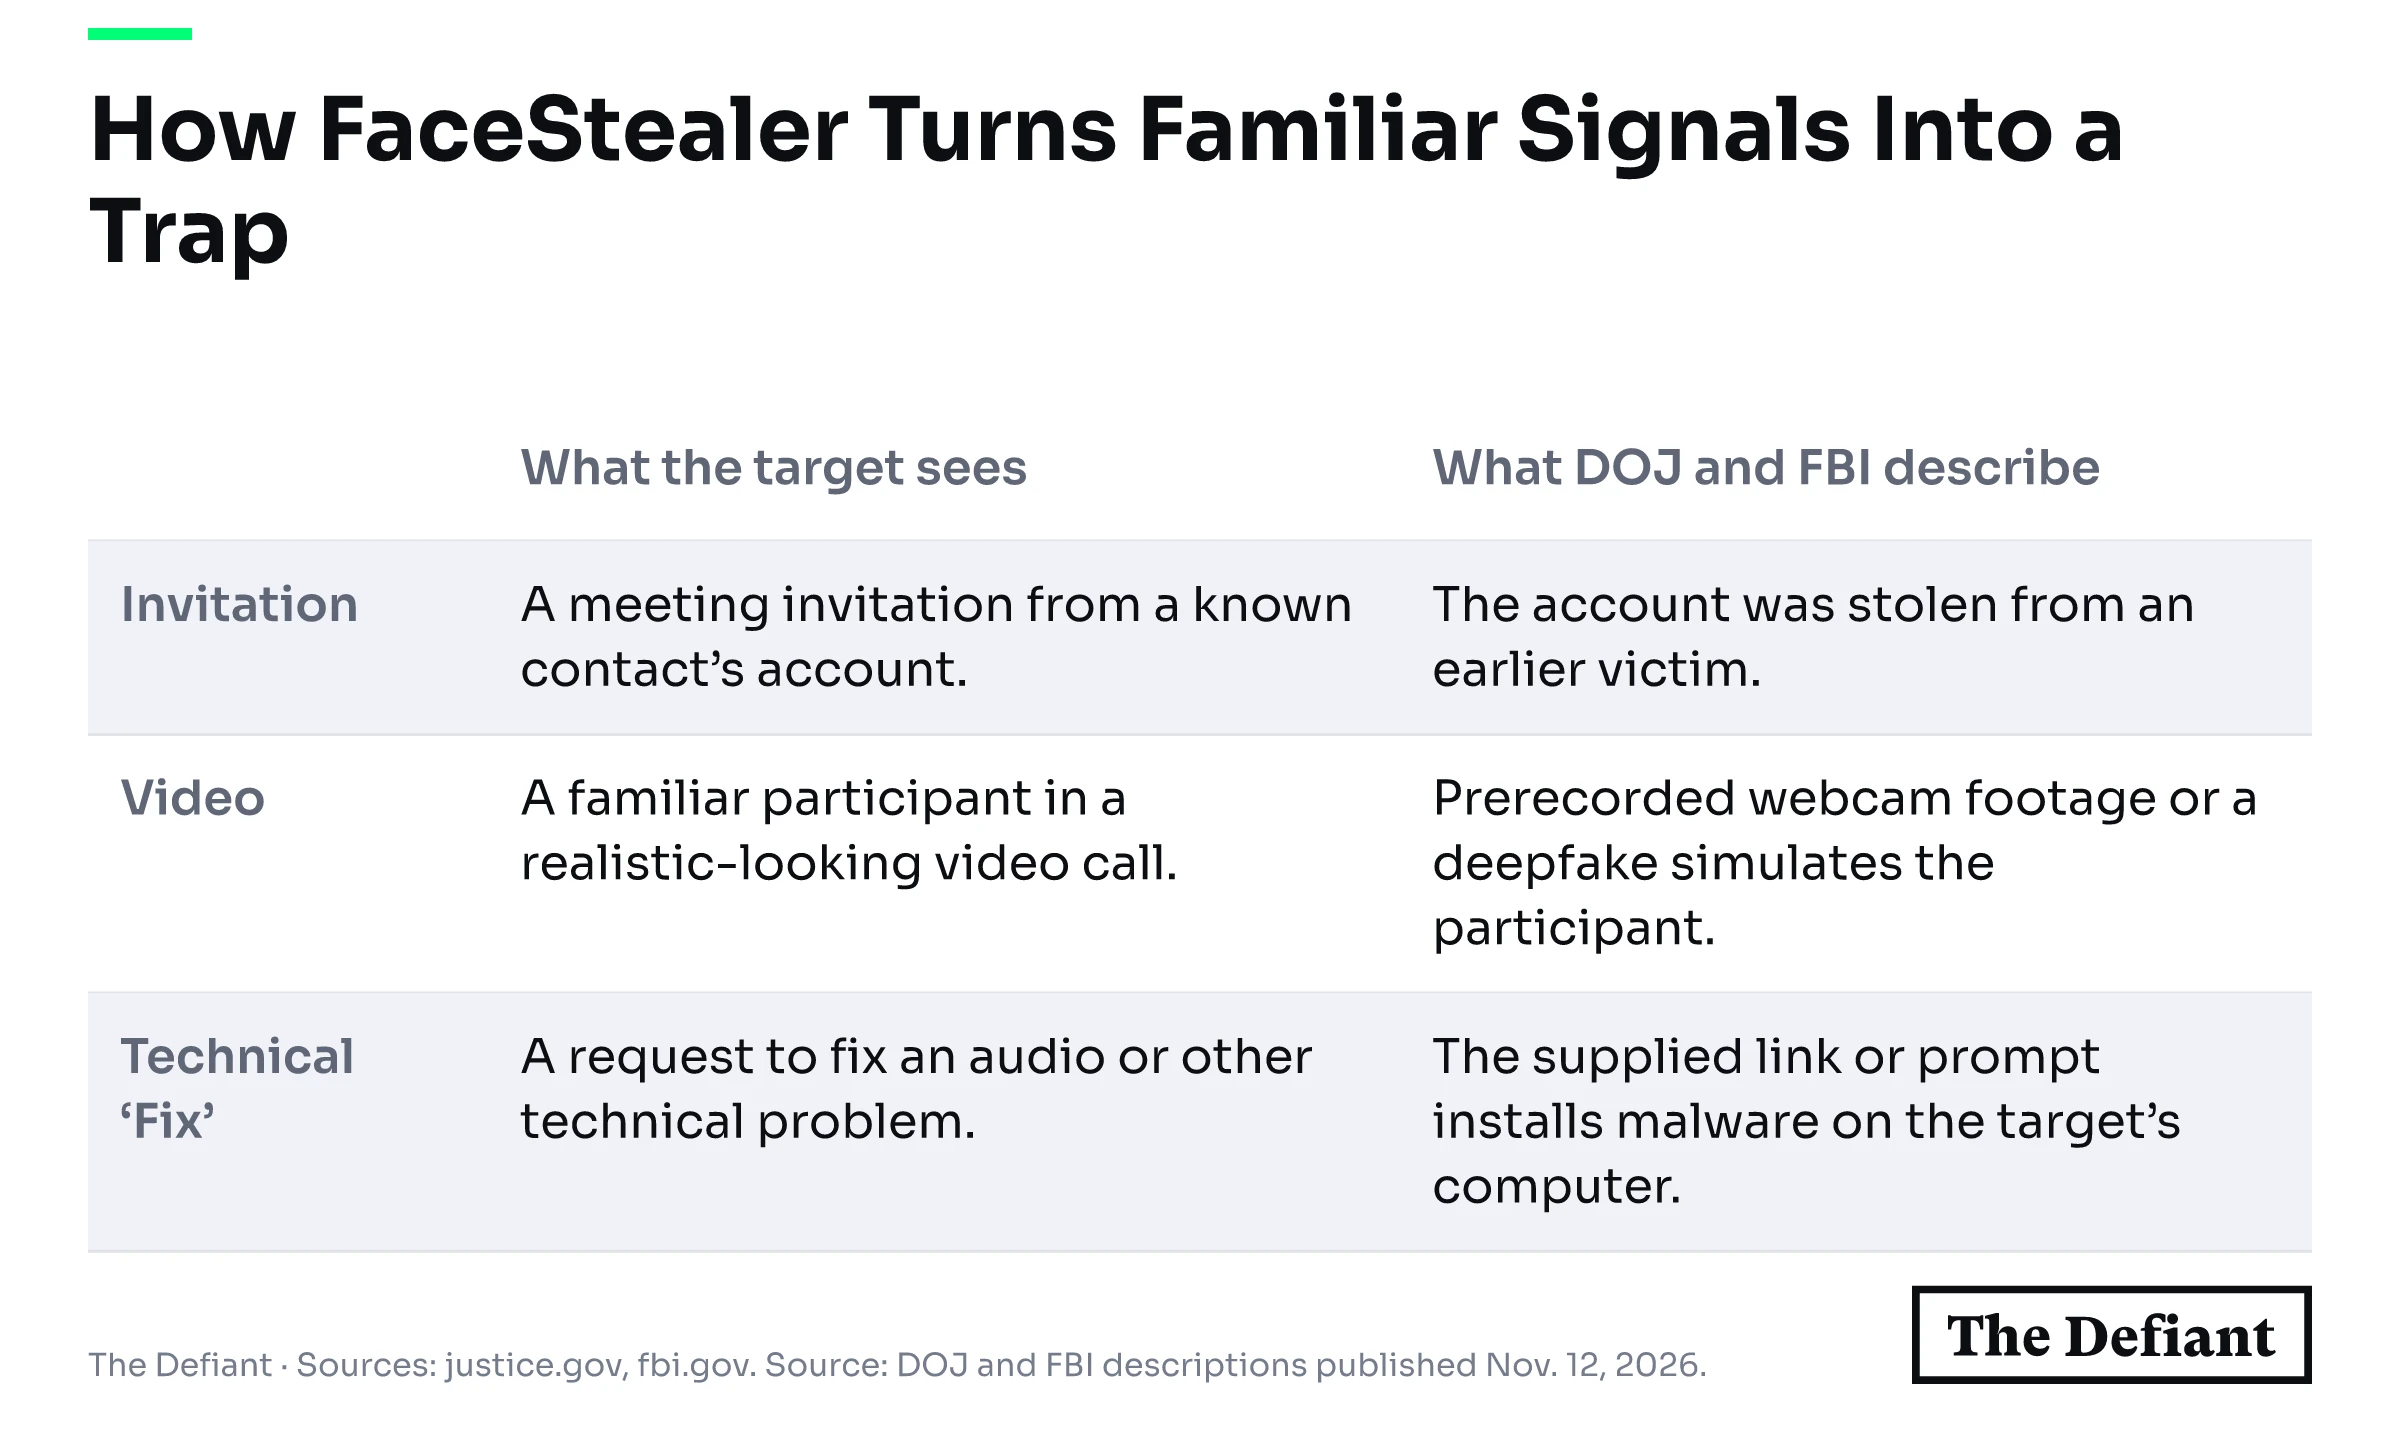
The campaign, which the FBI calls FaceStealer, uses accounts stolen from earlier victims to invite their contacts to meetings, according to the department’s Nov. 12 announcement. Attackers play secretly recorded webcam footage of people the target knows, or deepfake videos of prominent crypto figures, to make the meetings appear genuine.
“It exploits our trust in ubiquitous video conference platforms and valued personal relationships,” said Patrick Grandy, assistant director in charge of the FBI’s Los Angeles Field Office, in the announcement.
Know when your coins move
Alerts, real-time prices, and market news — all in one app
Point your phone camera to install
4.8 based on 40K reviews in the App Store and Google Play
During the call, attackers claim there is a technical problem—such as the target’s audio not working—and supply a link or prompt to fix it. That supposed fix installs malware on the target’s computer, the DOJ said. The FBI’s FaceStealer resource page describes the use of realistic imposter versions of video-conferencing platforms.
How FaceStealer Turns Familiar Signals Into a Trap
The exposure extends beyond an individual’s crypto holdings. The DOJ said attackers can exploit a compromised user’s access to other computer infrastructure and increasingly target open-source developers and maintainers to gain access to software repository accounts. That targeting appears intended to enable software supply-chain attacks, the department said—potentially reaching users of the affected software, according to the FBI.
The FBI seized more than 900 webcam videos of FaceStealer victims under a federal warrant, the DOJ said. Attackers also take victims’ contact lists and communications accounts to approach the next set of targets. In several reported cases, crypto theft and account hijacking occurred months to more than a year after the initial compromise, the department said.
The video-call lure builds on a pattern the FBI warned about in September 2024, when it flagged requests to run scripts to enable calls as a potential sign of North Korean social engineering. As The Defiant reported at the time, DeFi employees were among the targets. That earlier advisory recommended verifying contacts through separate, unconnected communication platforms and restricting which files company devices can download or execute.
Separate Action Targets Stolen Binance Assets
In the same announcement, the DOJ said it had obtained court authorization to seize or restrain more than $1.2 billion in assets tied to a separate Binance theft. That amount is part of more than $2.7 billion frozen through government and private-sector efforts, not an additional recovery on top of it.
The FBI attributed that theft of more than $6 billion on or about Oct. 29 to North Korean activity it calls TraderTraitor. The DOJ explicitly distinguished it from FaceStealer.
Efforts to trace, freeze, seize and forfeit the Binance assets remain ongoing as the attackers launder funds through bridges, mixers and exchanges, the DOJ said.

 thedefiant.io