Across Protocol warns users to avoid app amid reports of drained wallets
cointelegraph.com
11 m
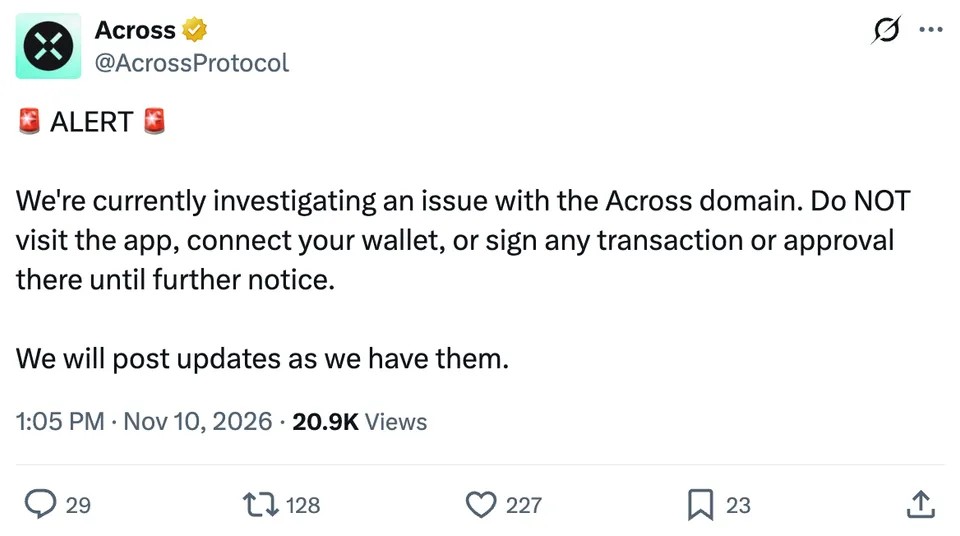
Crosschain bridging protocol Across, which allows users to transfer digital assets between Ethereum and other blockchain networks, warned users Tuesday not to access its app or connect their wallets while it investigates a potential security incident.
In a Tuesday X post, Across advised users against signing transactions or approvals until further notice, without specifying the nature of the incident or whether its website had been compromised.
Know when your coins move
Alerts, real-time prices, and market news — all in one app
Point your phone camera to install
4.8 based on 40K reviews in the App Store and Google Play
Source: Across Protocol
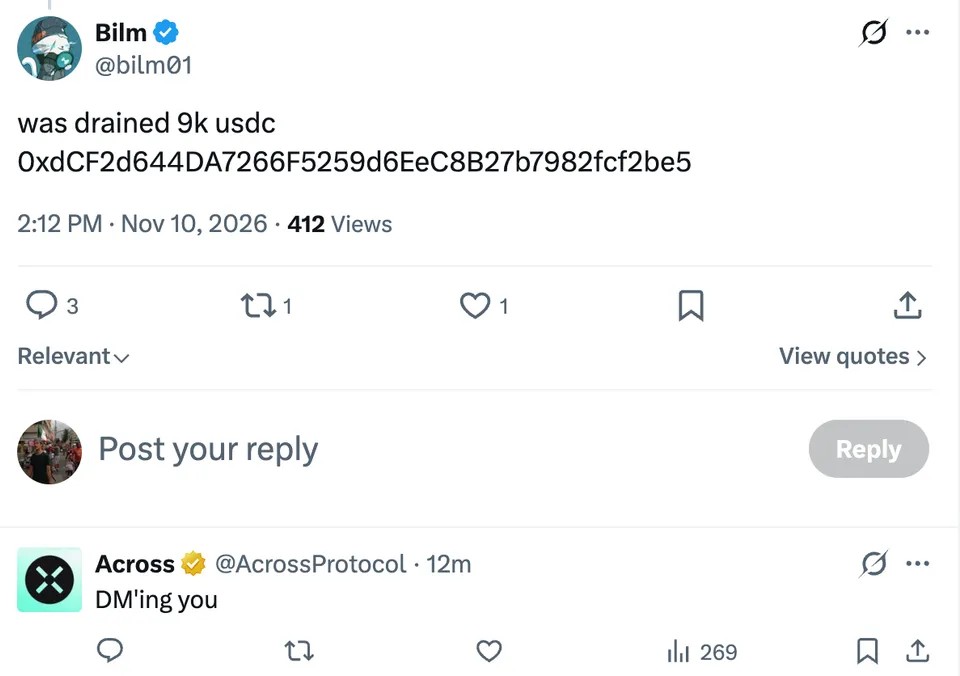
On X, one user claimed to have lost $9,000 in $USDC, while another reported losing 7,053 USDT0 across seven transactions on the Plasma blockchain.
A third user said their wallet was drained after using the bridge several times, alleging that the website had been compromised. Across asked the users for transaction details to investigate their reports.
Cointelegraph has not independently verified the reports. Across Protocol did not immediately respond to Cointelegraph’s request for more details.
Across Protocol responds to user reporting $9,000 $USDC loss. Source: X user bilm01
$NEAR AI discloses separate security breach
In a separate security incident, $NEAR AI disclosed Monday that attackers exploited a vulnerability in its AI infrastructure, exposing account details belonging to approximately 100 users and data from 18 AI agents.
According to a Nov. 9 incident report, attackers exploited a remote code execution vulnerability in SGLang, an open-source AI inference engine, to gain access to an internal server and other infrastructure. The compromised data included user names, email addresses, agent chat histories, settings and logs, while two customers had API keys exposed.
$NEAR AI said attackers may also have observed requests processed on the compromised server, including those running in confidential mode. The company said it had patched the vulnerability, revoked exposed credentials and restored access to its cloud services.

 cointelegraph.com