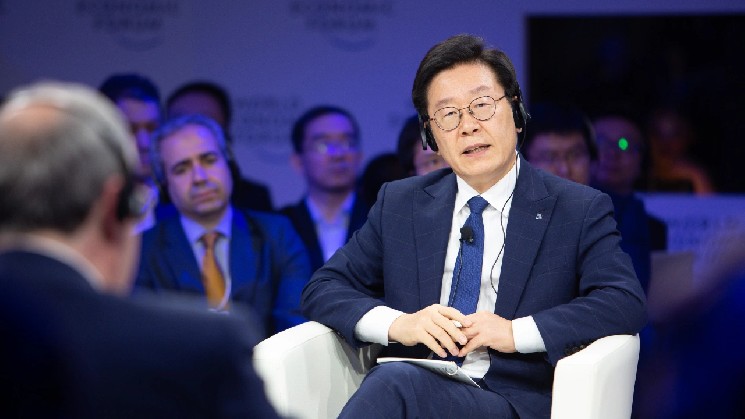
He asked officials to “actively consider forming a powerful and effective cybersecurity ‘tsar’ body” that would lead and organize security work that is now spread across many government offices.
Lee also said the country should consider a task force that includes both government and private companies. He pointed out that AI is making hacking smarter and more common, so the goal is to stop attacks before they happen.
He mentioned that the finance, energy and information networks are key areas that need stronger protection.
Officials must still decide what the security agency would look like and which powers it would take over from other offices.
Why is South Korea worried about cybersecurity now?
The main trigger for the request is the October 29 Binance theft, where a hacker took about $6.3 billion from the exchange’s online “hot” wallets across ten blockchains, most of it in about 20 minutes. TRM says it is the largest crypto theft ever, about four times the $1.5 billion Bybit hack in February 2025.
The FBI blamed North Korea on October 31, and TRM linked the attack to a North Korean hacking unit called TraderTraitor.
Cryptopolitan reported that North Korea has so far denied the attribution, with Kim Yo Jong, the sister of leader Kim Jong Un, calling the claim “absurd rhetoric and nothing new.”
Beyond the Binance hack, several Korean financial firms have been hacked recently, including Mirae Asset Global Investments, crypto exchange Bithumb and Daishin Securities (KRX: 003540). Some of these attacks exposed customer data.
South Korea’s spy agency, the National Intelligence Service, has started emergency security checks at more than 2,100 ministries, local governments and public offices.
Cryptopolitan also reported that the Financial Services Commission called in staff from five Korean crypto exchanges, including Upbit, Bithumb, Coinone, DigitalX and Gopax, to check how ready they are following the Binance hack.
Under Korean law, exchanges must keep at least 80% of customer crypto in offline “cold” wallets. The Binance money was stolen from hot wallets, which are connected to the internet.
Korean crypto users may have less protection than Binance users because a bill on paying back users after hacks, the Digital Asset Basic Act, has not passed yet.
Meanwhile, Binance has restored services, covering the losses from the incident. Binance has said it funded about 95% of the stolen amount from its own reserves.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.

 cryptopolitan.com