
 news.bitcoin.com
Malicious Servers Turn Bitcoin Fee Bumps Into Theft
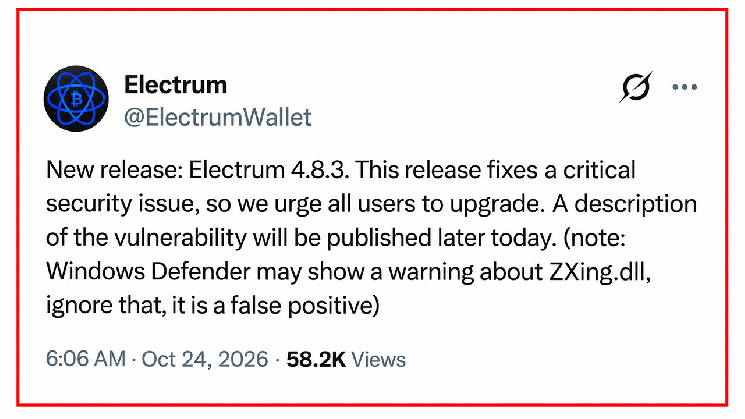
Electrum released version 4.8.3 on Saturday, warning users to upgrade immediately after developers discovered that malicious servers were exploiting a high-severity vulnerability affecting every earlier version. The flaw, documented in GitHub advisory GHSA-6jp4-8v48-cc5v, exploited how the lightweight Bitcoin wallet handles unconfirmed transactions.
Electrum relies on external servers for transaction histories, fee estimates, and broadcasting payments. While it independently checks confirmed transactions, older versions accepted certain unconfirmed transactions without verifying their signatures. Attackers turned that distinction into a trap.
A compromised server could intercept a legitimate payment, prevent its broadcast and substitute a fraudulent transaction directing funds to an attacker-controlled bitcoin address. The replacement carried invalid signatures, yet Electrum displayed it as an ordinary pending payment.



