Since a significant part of the classic internet runs on PHP (including WordPress platforms and systems running PHP-FPM), millions of web resources were put at risk. PHP developers promptly released security patches (in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35), but the panic also affected the cryptocurrency sector, where users are sensitive to any infrastructure risks and to a possible echo of this crisis.
Developers say the panic is unwarranted
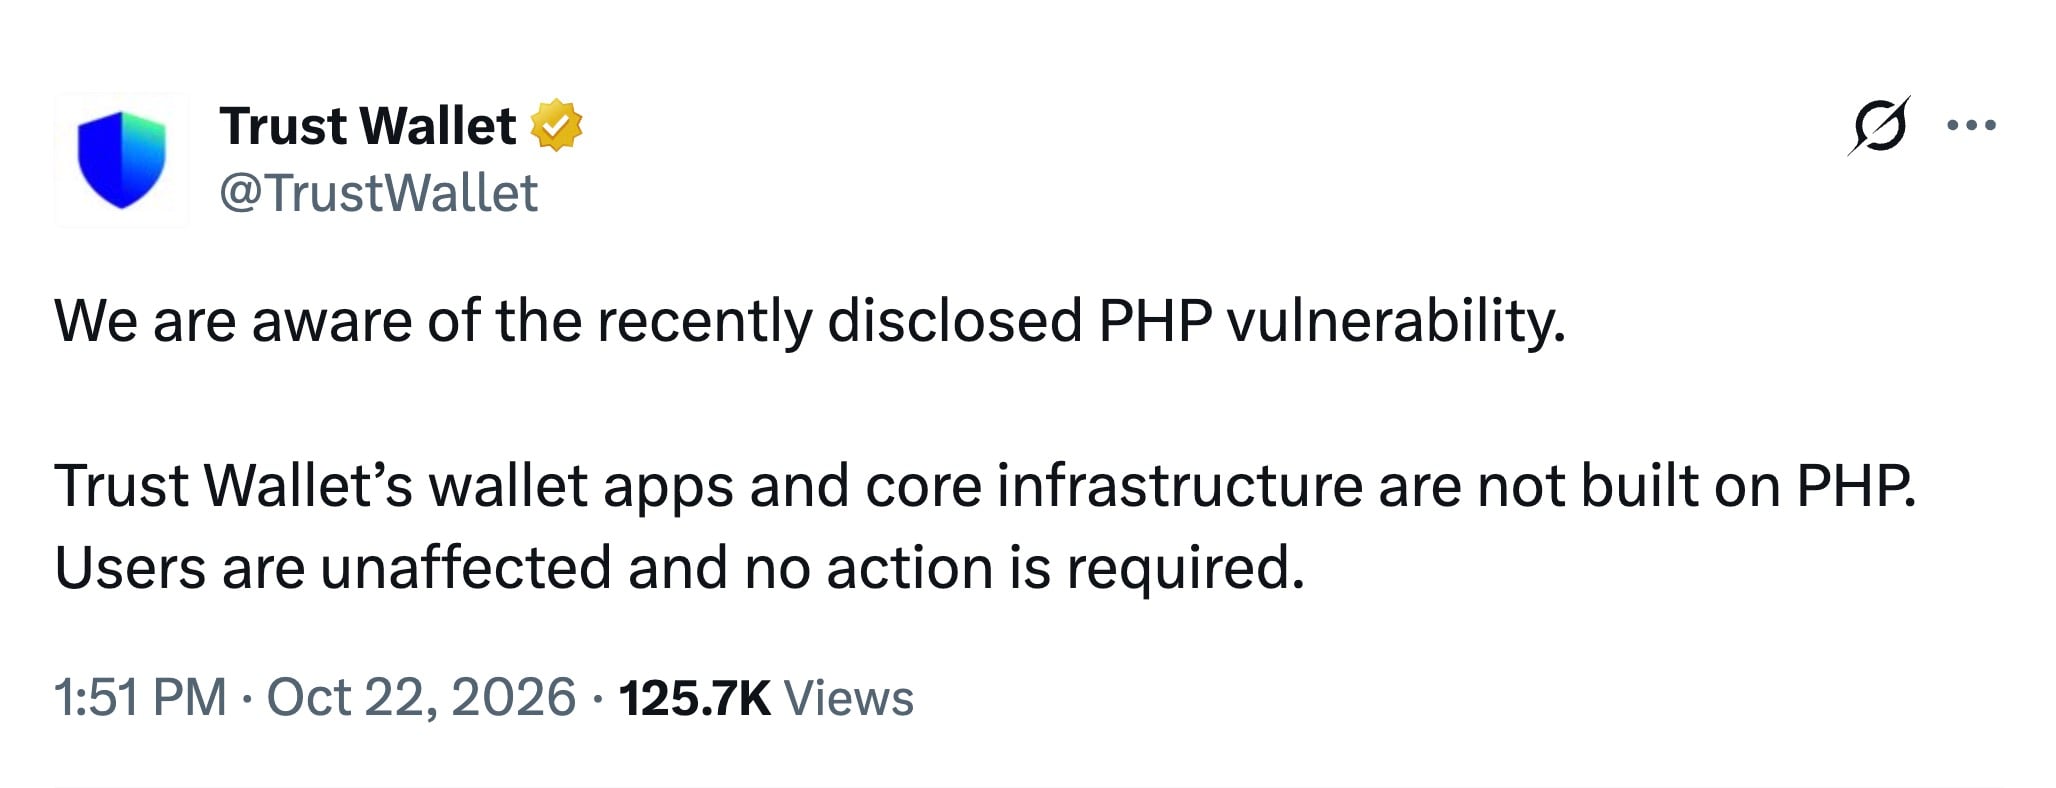
To stop the spread of rumors and completely eliminate speculation around the vulnerability (PHP exploit fallout), Trust Wallet published an official statement on X. In the post, the team directly stated that its applications and key infrastructure are not related to PHP, so the incident does not affect the wallet's clients in any way.
The technology stack of decentralized wallets is isolated from the PHP architecture, so the company's move was preventive. Earlier, similar statements about the absence of PHP in their ecosystems were issued by representatives of $BNB Chain and the decentralized exchange PancakeSwap.
The situation was noted by Binance founder Changpeng Zhao (CZ), who published a series of posts. He emphasized that most projects should at least publish such confirmations, since silence during global IT outages only gives rise to false rumors and sows panic among users.
No crypto wallet is 100% safe. No software is bug free. No tech is 100% secure. There are risks in everything you do. There are risks if you don't do anything. There will be issues, setbacks and problems to solve. Stay up-to-date. Manage risks. Solve problems.
— CZ 🔶 $BNB (@cz_binance) October 22, 2026
At the moment, the only threat to cryptocurrency holders remains the possible activation of phishers, who may use the news backdrop around the vulnerability to send out malicious "security updates."

 u.today