
 coindesk.com
Crypto swap platform $NEAR Intents calls itself permissionless, open and uncensorable. Yet it slammed the doors when stolen funds from Bitget tried to move through the protocol.
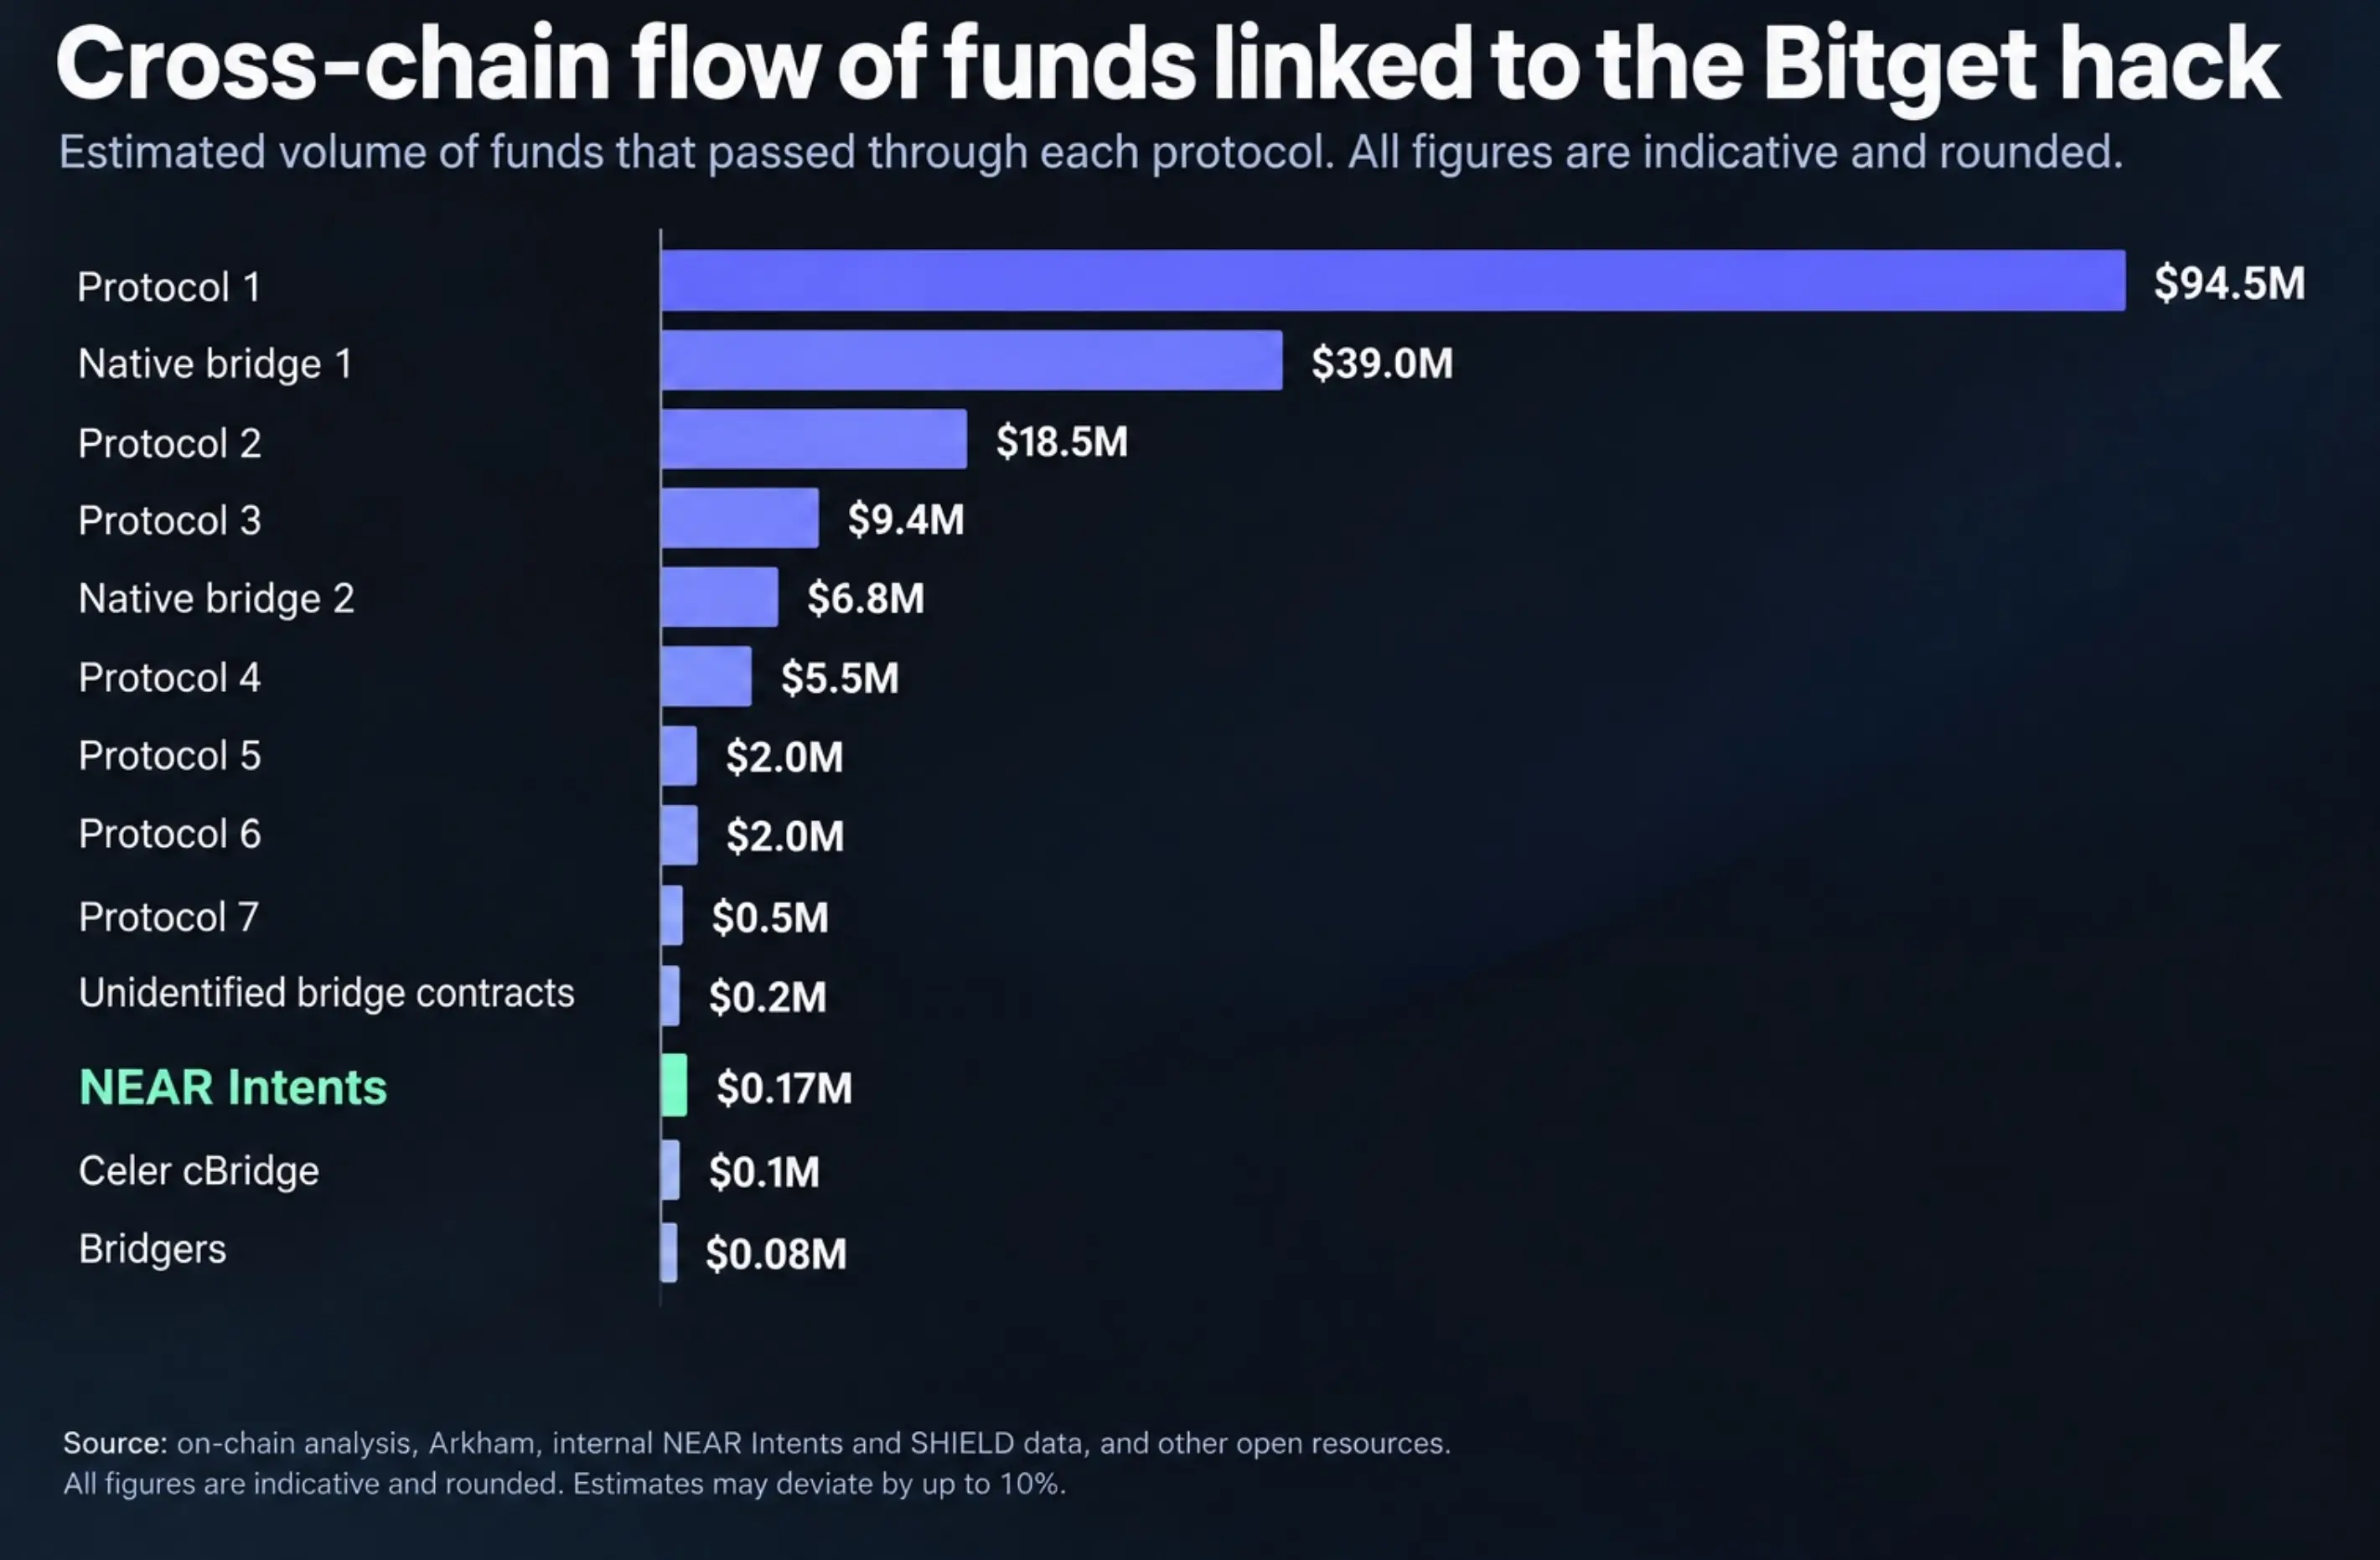
The attackers who siphoned off $388 million from Bitget exchange last week tried to move more than $50 million through $NEAR Intents, a service that lets users exchange assets across different blockchains, according to a report by $NEAR Intent’s general manager, Alex Shevchenko.
The protocol’s “SHIELD” system blocked most transfers and froze $503,000 midway through the transaction, taking a different approach from THORChain, which has resisted the exchange’s request to block attacker addresses.
About $166,000 passed through, while the restricted funds await a legal and recovery process, he said. The larger figure represents attempted transfers rather than money recovered.
Shevchenko said duplicate attempts had been removed from the tally and rejected funds subsequently went to other providers. The figures are estimates, however, and could differ from the actual amounts by up to roughly 10%.
“$NEAR Intents routinely processes $100M+ of a crosschain trading volume in a day. Yet in this case, only a negligible fraction of the hacked funds were flowing through us,” he said.
“The reason for this behaviour is SHIELD. It automatically detects deviations in flows, collects numerous inputs from KYT and intelligence providers, independent researches, companies and largest centralised players in the industry. Based on these signals the protocol can decide how to handle a transaction,” Shevchenko added.
In other words, permissionless and open doesn’t automatically mean a free ride for malicious actors and their money.
Bitget disclosed the breach on Sept. 24 after attackers bypassed security controls protecting its exchange wallets. The company has since said it fixed the vulnerability, published attacker addresses, and offered bounties for eligible efforts to freeze or recover funds.
Circle and Tether, the issuers of USDC and USDT, have already frozen about $320,000 in stablecoins linked to the breach, as CoinDesk reported last week.
Intents documentation says the service checks swap requests for links to reported hacks and can delay suspicious transactions. These checks apply when someone uses the swap service, but do not give its operators control over every wallet on the $NEAR blockchain.
The ability to hold funds has drawn scrutiny of $NEAR Intents’ description of itself as permissionless, meaning people can use it without seeking an operator’s approval.
Who gets to stop a swap
The intervention drew criticism online over whether a service that can hold funds should describe itself as permissionless. Among those questioning the label was Vini Barbosa, a technical writer and documentation engineer building at Ramp Labs.

