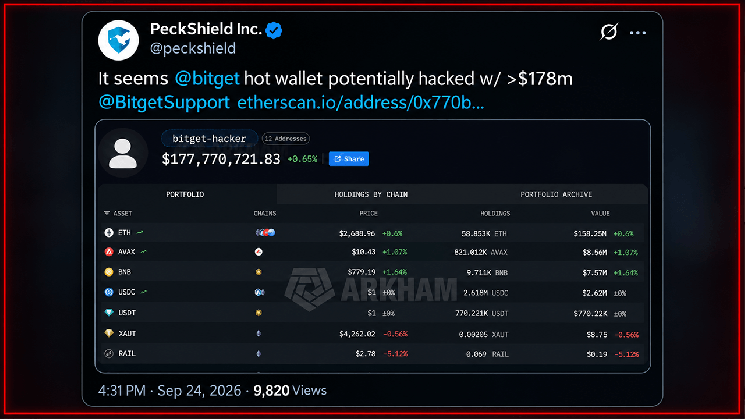
In a security notice, Chen said Bitget’s systems detected unauthorized transfers at 18:31 UTC on Sept. 24 and that its security team activated emergency protocols “immediately.”
Bitget estimates approximately $351.6 million was affected. Chen stressed that the exchange’s cold wallets remain secure, saying the incident was contained to portions of Bitget’s hot and warm wallet layers within its three-tier wallet architecture. The exchange has temporarily suspended withdrawals while it conducts a security review. Deposits and trading remain operational.
Bitget Says $464M Protection Fund Covers Loss
Perhaps the biggest number after the $351.6 million itself is $464 million. Chen said Bitget’s User Protection Fund currently holds more than $464 million and that the entire estimated loss falls within its coverage. According to the exchange, user account balances remain accurate and customer assets are protected.
Bitget said its emergency response team was activated within minutes of detecting the transfers. Addresses associated with the abnormal movements have been identified, flagged and reported, while law enforcement and onchain security firms have been formally notified.
Earlier in the day, security firms Hacken and Peckshield had drawn attention to suspicious movements involving Bitget-labeled wallets. At the time, however, no official confirmation existed that the transactions represented theft.
That uncertainty is now gone, although one major question remains unanswered: how did the attackers get in? Bitget said it would not speculate about the attack vector while its investigation is underway. Chen promised hourly updates through official channels and said a complete incident report, including the root cause and corrective measures, will be published within 24 hours.
For now, withdrawals remain paused as investigators work backward through one of 2026’s largest confirmed crypto exchange security incidents.

 news.bitcoin.com