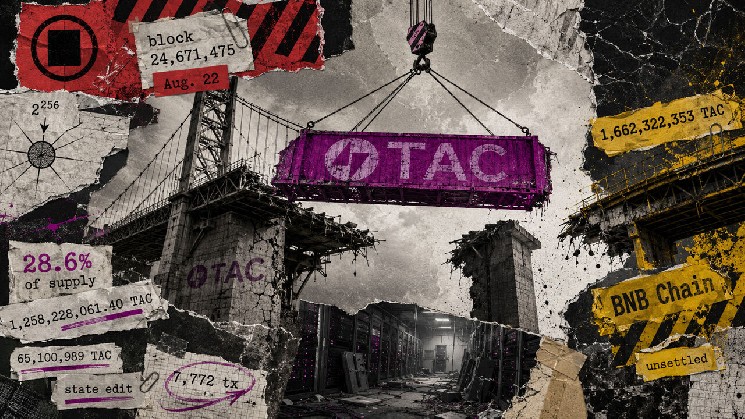
Cosmos Labs said a second overflow operation then let an attacker zero a victim account while retaining its legitimate tokens. TAC identified the protocol-controlled staking pool as the victim account on its network. The advisory classed the flaw as critical and said Cosmos EVM versions below 0.6.2, plus versions 0.7.0 and 0.7.1, were vulnerable.
The disclosure trail predates the attack. Cosmos Labs' postmortem said the bug reached its bounty program on April 25, was patched on the main branch May 15 and was backported into releases on Aug. 19. A Push Chain fork publicly described the path on Aug. 20. TAC separately said it sent a maintainer an analysis of two related defects in July without acknowledgement.
TAC network halt recovery leaves $BNB Chain balance unresolved
TAC said the attacker sold 1,208,329,197 TAC on $BNB Chain for 950,293 $USDT and another 49.9 million TAC on TON for 55,481 $USDT. The reported proceeds total 1,005,774 $USDT.
The proposed recovery splits the drained pool three ways. A targeted state edit would remove 65,100,989 incident-linked TAC frozen on TAC. Another 1,662,322,353 TAC remains in incident-associated $BNB Chain addresses and will be handled separately. TAC said the remaining 1,258,228,061.40 TAC, representing tokens sold from the pool, would be replaced in full from TAC Foundation treasury reserves.
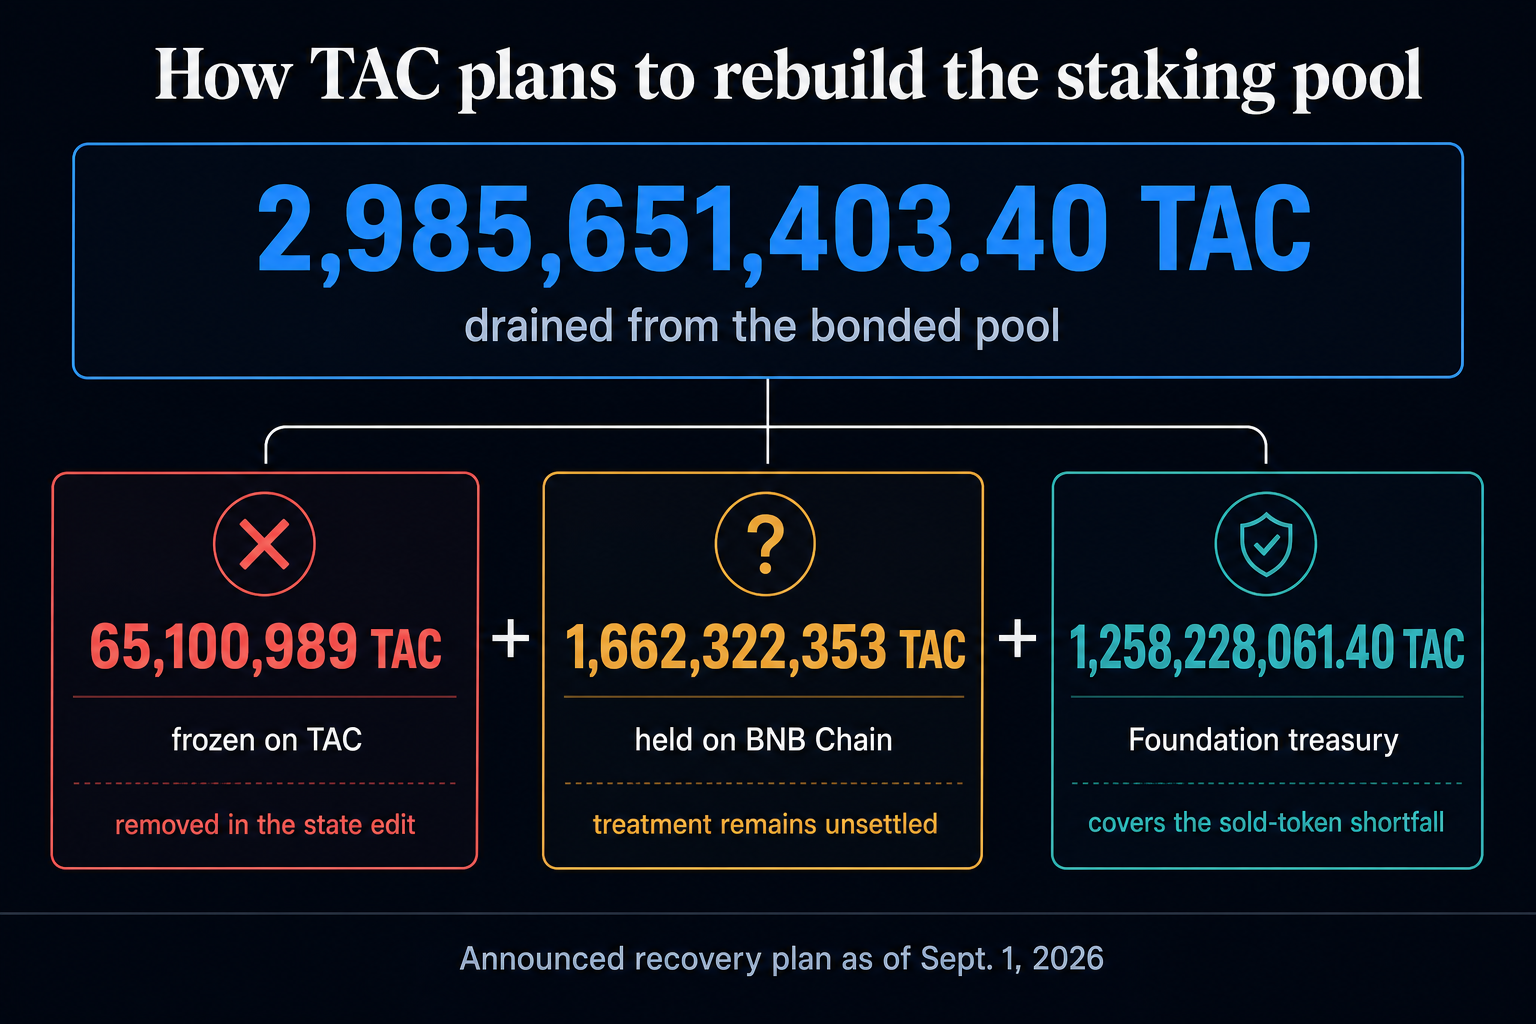
Unlike a rollback, the proposed edit would correct specified balances at the halt block without rewinding the chain. TAC said that would restore the bonded pool and delegator balances while preserving 7,772 legitimate transactions from 218 unrelated addresses.
Ending the TAC network halt still depends on validators adopting TAC's patched binary, resuming block production and executing the edit. Bridging and redemption remain disabled, and TAC has not settled how the 1.662 billion TAC on $BNB Chain will be treated. The treasury commitment therefore addresses the sold-token shortfall, not the larger attacker-held balance outside the network.

 cryptoslate.com