cryip.co
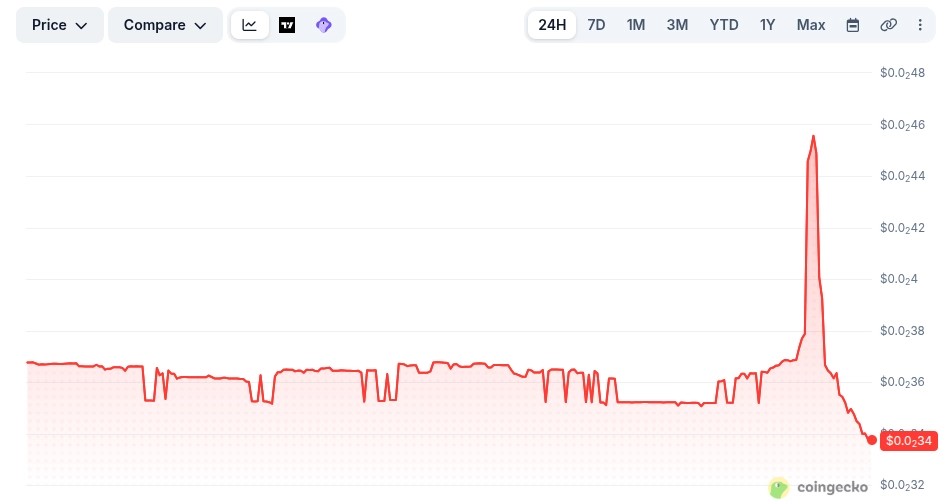
An attacker forced Moonwell’s price oracle to overvalue MAMO, then used the inflated token as collateral to borrow cbBTC from the protocol’s Base lending market. This is Moonwell’s third security incident in nine months. Each one involved an asset whose price could not yet be fully trusted, and each time that asset was allowed to do something consequential anyway, whether holding governance power, backing real collateral, or pricing a loan.
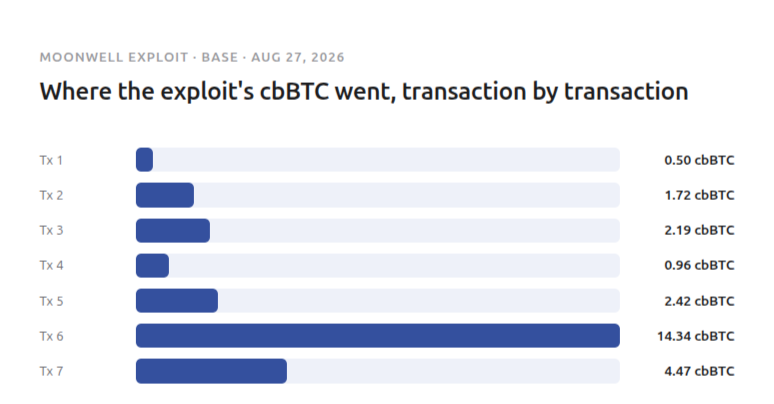
The attack began at 08:43 UTC on August 27, 2026, and was still unfolding hours later, with no official response yet from Moonwell. Blockaid, the security firm that first flagged the activity, said the attacker inflated the price Moonwell’s oracle assigned to MAMO, letting a relatively small amount of the token pass as collateral worth far more. That let the attacker draw cbBTC out of the mCBTC market, a pool meant to be backed by real Bitcoin exposure.
Blockaid’s Exploit Detection identified suspicious activity against @MoonwellDeFi on Base.
An attacker manipulated MAMO collateral pricing to borrow cbBTC from the mCBTC market.
Observed impact so far: 50.6 cbBTC ($4.0M+) drained
More details to follow.— Blockaid (@blockaid_) August 27, 2026