Cloudflare Adds Ruby2Shell Rules; Ruby Patch Still Needed
thedefiant.io
3 h
Cloudflare said on Nov. 20 that it added web application firewall (WAF) rules against ruby2shell (CVE-2026-132825) across all plan tiers. The default-block rules run automatically on Free plans; paid sites are covered where the Cloudflare Managed Ruleset is deployed and the rules have not been overridden.
Ruby's maintainers rate the flaw Critical and say specially crafted strings can cause memory corruption that may let an attacker run code on a server. They know of proofs of concept that achieve code execution in some scenarios.
For crypto-platform and DeFi front-end operators using affected Ruby software, the patch target is the Ruby runtime itself. Cloudflare describes its filtering as a stopgap, not a replacement for that fix.
Know when your coins move
Alerts, real-time prices, and market news — all in one app
Point your phone camera to install
4.8 based on 40K reviews in the App Store and Google Play
In a Nov. 19 technical disclosure, researcher Moritz Sanft described how a form field used to override an HTTP request's method reaches Ruby's string case-conversion code through Rack, a component used by Rails. Certain legacy character encodings can make that code write one byte beyond its allocated memory buffer. Cloudflare says the request reaches the vulnerable code before application authentication runs.
Veria Labs, which independently found the vulnerability, says default Rails and classic-style Sinatra applications expose this path. Other frameworks and plain Rack applications are not exposed by default, though application code that changes the case of attacker-controlled strings in a legacy encoding may also be vulnerable.
Patch Ruby Beyond the Web Server
Affected releases in maintained branches are Ruby 3.3.0 through 3.3.13, 3.4.0 through 3.4.12, and 4.0.0 through 4.0.9. Veria Labs traces the flaw in older branches back to Ruby 2.4.0. The Ruby security advisory recommends upgrading to 3.3.14, 3.4.13 or 4.0.10. Ruby 3.2 and earlier are no longer supported and will not receive these upstream fixes.
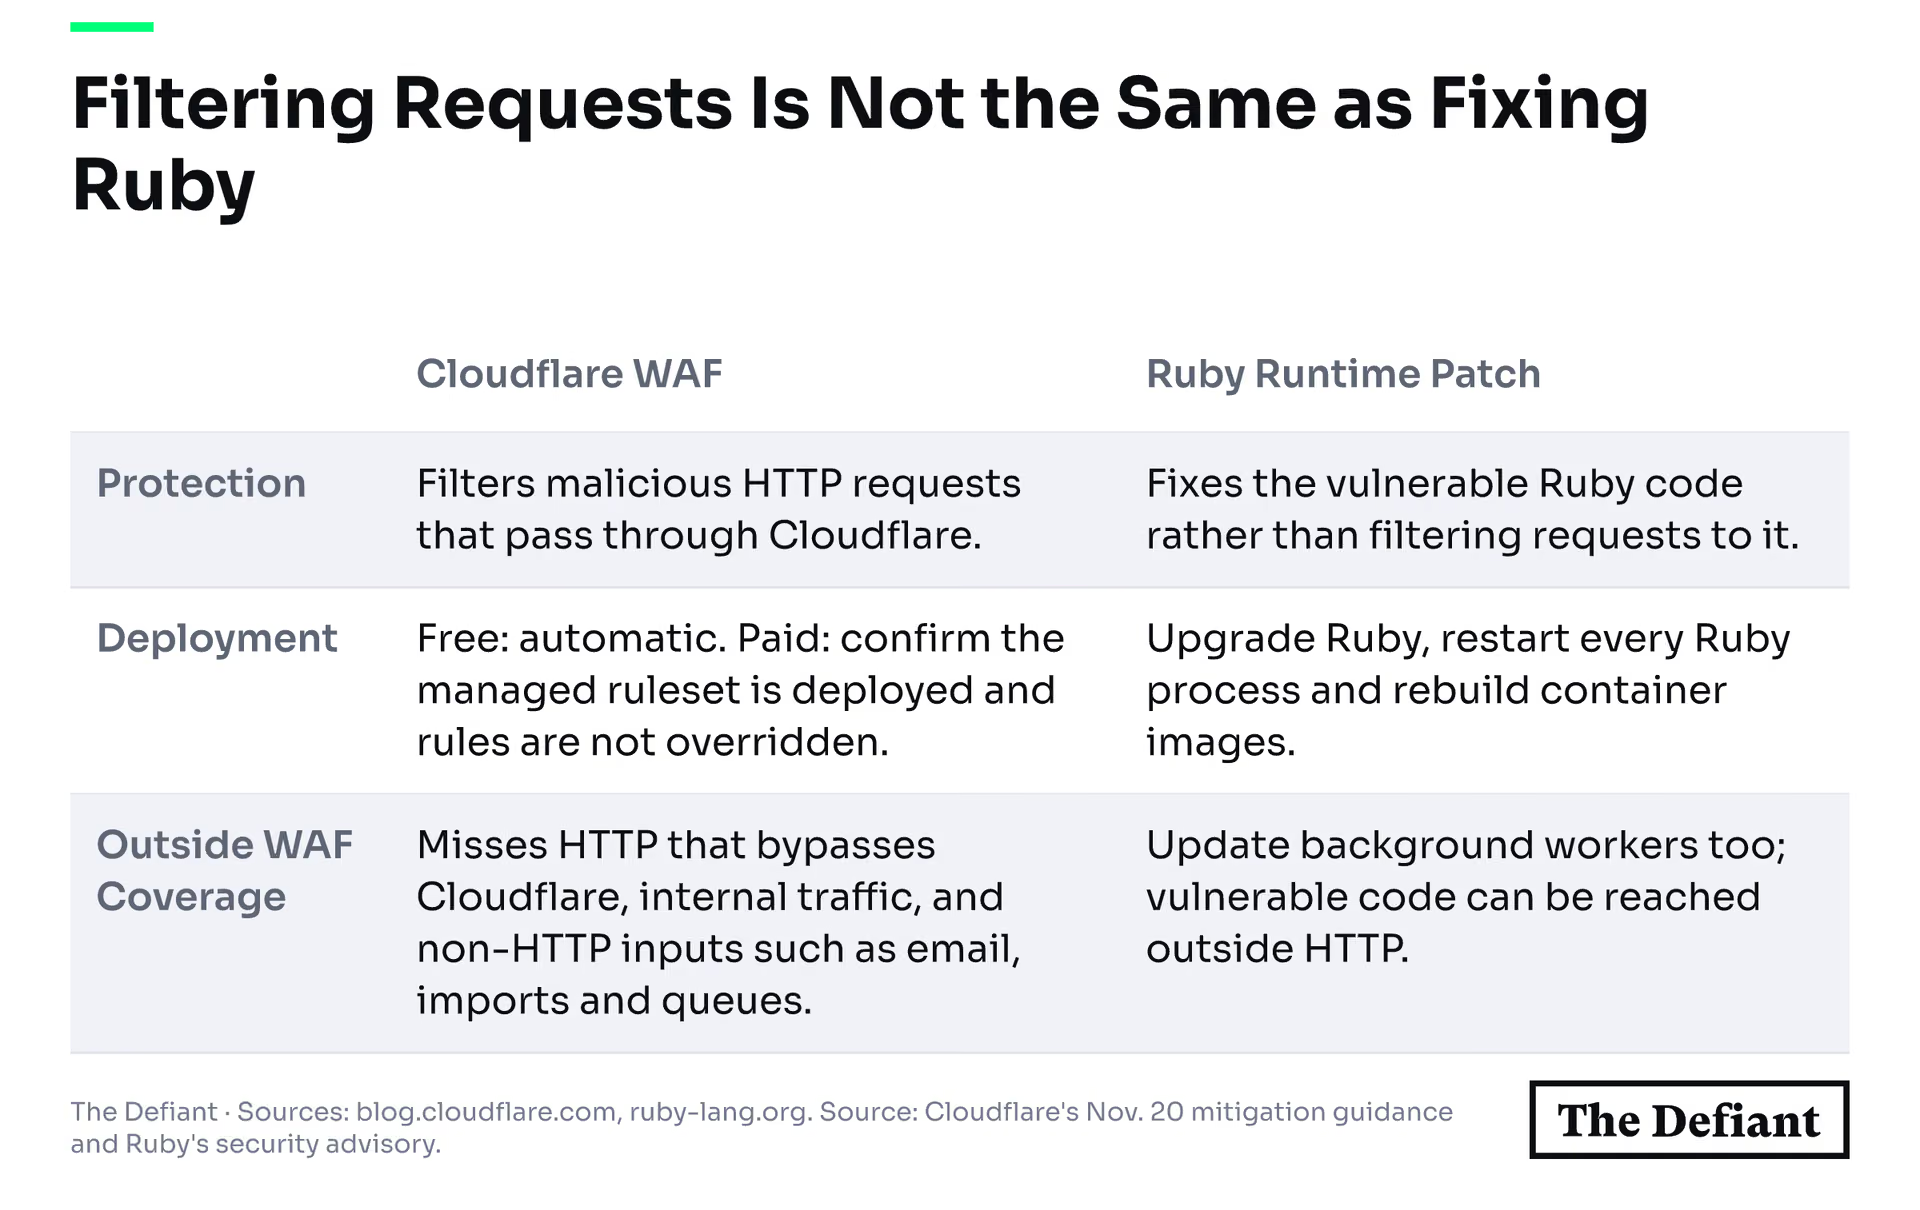
Cloudflare advises restarting every Ruby process, including background workers, after upgrading, and rebuilding container images. Distribution packages may carry backported fixes without changing the Ruby version number, so operators should check the full package version against their distributor's advisory.
The WAF only inspects HTTP requests passing through Cloudflare. Direct-to-origin traffic and non-web inputs fall outside that shield, the company warns.
Filtering Requests Is Not the Same as Fixing Ruby
Veria Labs says it plans to publish a proof of concept demonstrating code execution on stock Rails on Nov. 25, or later if major vendors have not shipped fixes by then.

 thedefiant.io